Security & privacy
Your money records, kept safe
Your records are stored on our server, and they stay yours: export anytime, delete anytime, never sold. Here is what we do, in plain words, and what we are still working on.
Locked every time you open it
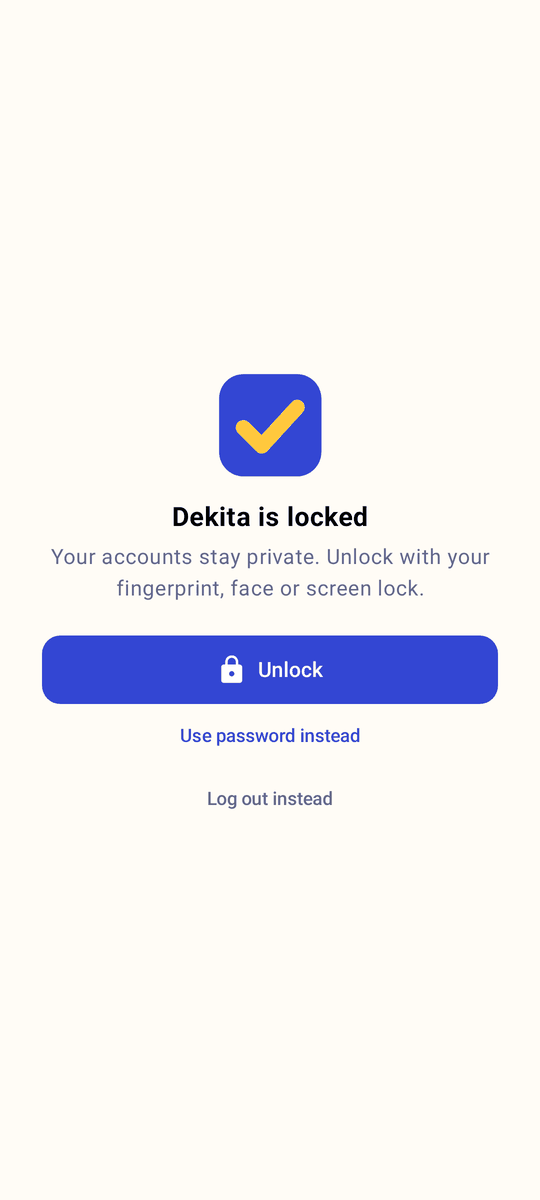
Dekita asks for your fingerprint or password every time you open it. It locks again the moment you leave, turn off the screen or switch apps. There is no way to switch app lock off.
On your phone
- App lock, always: Dekita asks for your fingerprint or password every time you open it, and locks as soon as you leave. Your sign-in token is encrypted with an Android Keystore key that only opens after you unlock.
- No screenshots: screenshots and screen recording are blocked inside the app, and the recent-apps preview stays blank.
- Card numbers: Dekita keeps only a card’s name and last 4 digits. Anything that looks like a full card number is refused.
- Not in phone backups: app data is excluded from cloud backups and device transfers. Exports are saved only where you choose.
On our server
- HTTPS only: every connection between the app and our server is encrypted.
- Passwords: stored as Argon2id hashes. We never see or store your password itself.
- Every account walled off: our PostgreSQL database uses row-level security, so one account can never read or change another’s records. The database is not exposed to the internet.
- Sign-in protection: repeated wrong passwords slow down further tries, per account and per IP address. Sessions end after 90 days at most.
- No money data in logs: database logs never include the amounts or details you enter.
Backups
- Backups are taken every day, and an encrypted copy is made with age. The key to open it is not kept on the server.
- An encrypted off-site copy in Google Drive is being set up. It will be encrypted before upload, so Google can’t read it.
- Backups roll off after 14 days, so after you delete your account, your data is gone from backups within 14 days too.
What we never do
- No advertising, analytics or tracking SDKs.
- We never sell or share your data.
- We never ask for bank, card or wallet logins.
- We don’t read your contacts, SMS, location or photos.
What we’re still working on
- Dekita is in early access. Two-step sign-in (2FA) isn’t available yet.
- The live database disk isn’t encrypted at rest yet. Encrypting stored data and off-site backups are both in progress.
- Dekita is not end-to-end encrypted: to work, the app keeps your records on our server. That’s why we take access control, backups and deletion seriously.
This website
- No cookies, no analytics and no third-party scripts. Fonts and images are served from our own server.
- Strict security headers: HSTS, a Content-Security-Policy with no inline scripts, frame-ancestors none and nosniff.
- The waitlist stores your email, your country (optional) and a one-way hash of your IP address. We don’t keep the raw IP address.
Report a security issue
Found a weakness? Please email support@heydekita.com. We’ll reply quickly and let you know when it’s fixed. Please don’t access or delete other people’s data, and don’t disrupt the service. We won’t take action against good-faith research. There is no paid bug bounty at the moment. Machine-readable contact: security.txt.